
Windows 'IptabLeX Botnet Ddoser'
As discovered last week, a variant of the original is now infecting Windows machines. The CNC is on another site which is hosting a http:/..../getsetup.exe and then this spawns 2 versions of getsetup.exe
The site mentioned in the Anubis report is carrying the payload and delivering a executable which then installs the 2 windows services.
It's worth mentioning at this point that the CNC and domains are all listed here are present in the Windows version too, an initial query to the following dns.dsaj2a.com is made, i did not observe any further operations.

Anubis report mentions in detail the actions carried out & the researchers over at Malware Must die have today confirmed this here & here
Here is my Cuckoo analysis - which shows the infection.
Thanks to @malwaremustdie for their original investigations on the Linux variant.
Mac OSX 'iWorm'.
A very alarmist and misleading title from a web firm,
'' New Mac OS X botnet discovered "
Labelled as botnet, yet named as a 'worm'. What's interesting is the directory in which it allegedly drops into a JavaW directory, one assumes you may need to have Java installed*
Here is a link how to protect yourself, or an alternative.
All in all, not much investigation into the actual worm, no information on how it propagates either.
*I do not
Splunk Panels & CSS fun
I was given an requirement to deliver an analytics engine to display multiple sources of known Bad IP and domains in a somewhat attractive fashion, i am using LogRhythm for some of the metrics & Splunk for others.

The only issue with Splunk is the OOB configuration is quite bland, and comes with some quite simple CSS & HTML, but i didn't have the time to change these. The best solution is to install the Splunk 6.1 Example dashboards, and clone the 'Dark Panel'.
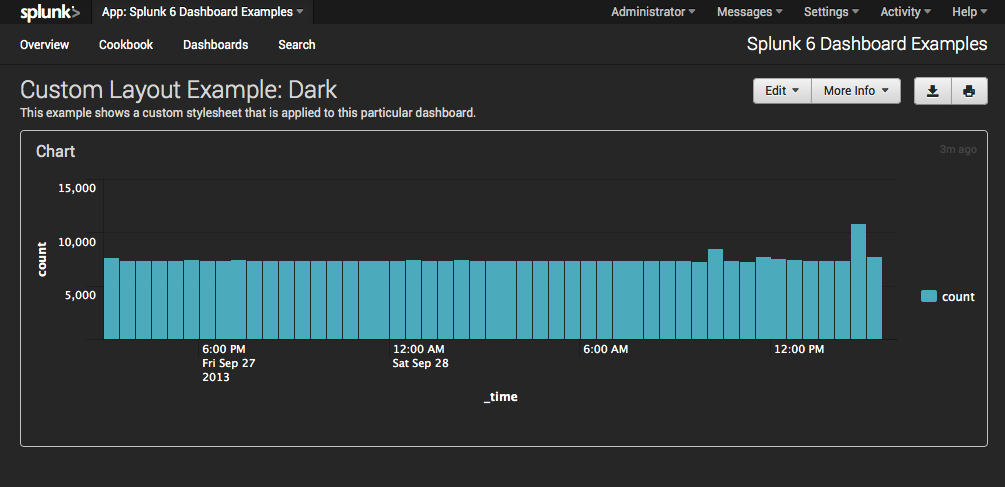
With some minor CSS changes, we can edit it to mimic the colours of the LogRhythm panel. i simply used Firebug for Mozilla and tracked the CSS and HTML.
Titan Internet multiple XSS
I've attempted to make them aware of the the multiple (11) XSS that are confirmed active on their hosting site, which include the transactional parts of the website including billing. I did disclose this to them over 4 days ago with no answer.
This is a claim from their 'vulnerability scan'.
- 'On September 14, 2011 secure-gateway.titaninternet.co.uk met the PCI data security requirements by passing a SecurityMetrics® Site Certification vulnerability scan.'
If you're a customer of this hosting company i would ask you to question whether they are conscious of this & what steps they are doing to protect the data they are holding.
OSX & 2fa thoughts
Apple will release a new version of OSX & iOS in the final Q of 2014, one of the features is the unification of SMS and subsequent delivery via OSX & iOS. This poses some interesting scenarios on the ability to maintain 2fa with such services as Google.
Google provide the ability to authenticate via a SMS to a chosen telephone number, of course the password is still required but this brings a potential new attack vector.
Responsible disclosures
Finding a vulnerability will excite some analysts, some will even go as far as disclosing it for free. Do not ever do this unless you're willing to handle the responsibility of fixing it. The reason we exist in this arena is to be able to find and expose vulnerabilities and risks, a responsible disclosure not only endorses you as a analyst it build your reputation.
Beats to be Apple
Can't help but think this would not have happened if Ping would have taken off.
On a serious note, the potential purchase of this particular market share shows Apple isn't afraid to spend the cash that it has amassed. Beats isn't a niche market, its not just the wearable market either. This market is full of streaming competitors, what Beats has is a customer base which has already approved of its service. A smart move considering the new iOS integration.
Latest Tweets